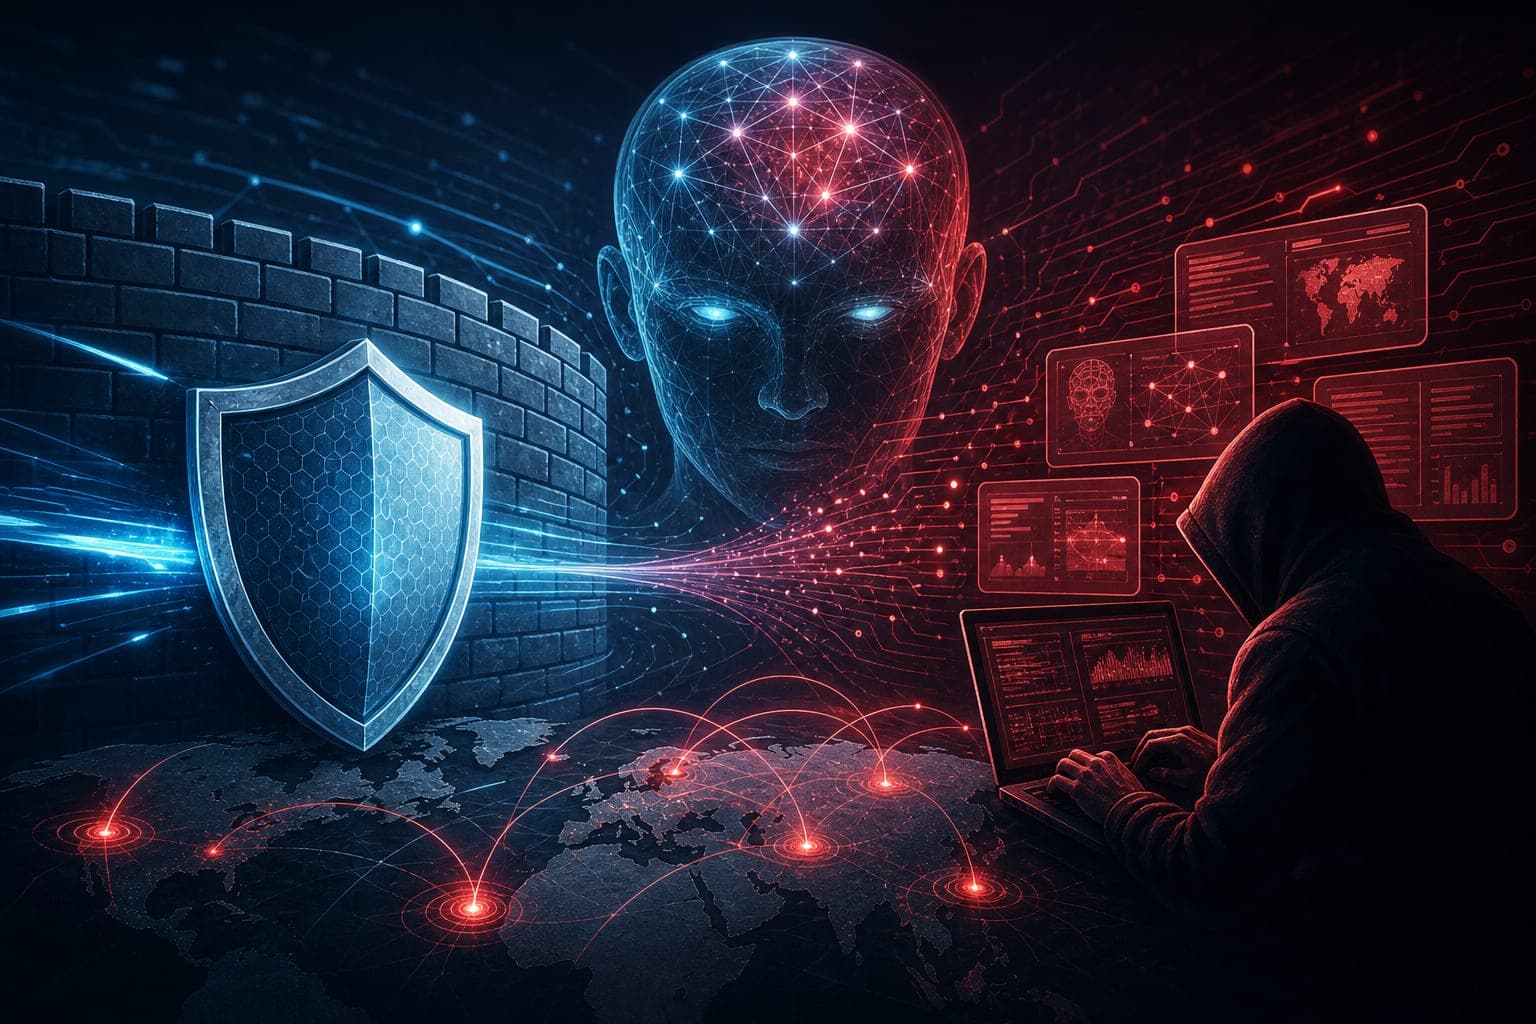
Seldom has a single technological development posed such a fundamental challenge to global cybersecurity infrastructure. The Federal Bureau of Investigation recently issued a FLASH advisory concerning ARTEX, an artificial intelligence platform now exploited by malicious actors. Originally conceived as a penetration testing framework, ARTEX has been repurposed to automate sophisticated cyberattacks at unprecedented speed. This alarming development underscores the dual-use nature of advanced technologies in contemporary society.
What distinguishes ARTEX from conventional hacking tools is its capacity for autonomous operation with minimal human oversight. The platform employs multiple AI agents that independently execute complex intrusion tasks. According to the FBI, some attackers have progressed from initial targeting to privileged access in under three hours. Researchers identified more than 1,600 publicly exposed ARTEX console instances by early November, illustrating its widespread proliferation.
The ramifications of this threat extend across multiple critical sectors. The FBI documented attacks targeting financial institutions, government agencies, defense contractors, and healthcare providers. In one notable campaign against South Korean financial institutions, personal data belonging to approximately 67,000 individuals was compromised. Furthermore, an October supply-chain attack involving ConnectWise Cloud Backup exposed vulnerabilities in Microsoft 365 customer environments.
The emergence of autonomous attack platforms represents what cybersecurity experts characterize as a critical inflection point. Such tools effectively lower the technical barriers to conducting complex intrusions. Consequently, even actors with limited expertise can execute sophisticated campaigns previously reserved for advanced threat groups. This democratization of cyberattack capabilities has profound implications for organizational security worldwide.
In response to this escalating threat, the FBI has urged organizations to mitigate their exposure by strengthening access controls. Monitoring unusual sign-ins and data transfers constitutes another essential defensive measure. Not only must institutions invest in robust cybersecurity infrastructure, but they must also cultivate a culture of vigilance. The advisory serves as a sobering reminder that technological innovation invariably carries both promise and peril.